They’re your cases. You stay in control.
Case records are some of the most sensitive information there is, and they get read by solicitors, deputies and courts. Clinical-grade security isn’t an add-on in Casely. It’s how the system is built.
Who can see what
You set access person by person and client by client. Someone working on one case doesn’t see another unless you say so.
That includes us. Casely staff can’t open your cases unless you choose to let them in, for example to help with a support question, and you can take that access away again.
Where your data lives
Your data is stored and processed in the UK. Each practice’s records are kept separate from every other practice’s, and nothing is read or written across regions.
Encryption
Records and files are encrypted with AES-256 when they are stored, and encrypted in transit between your device and Casely.
Every file you upload is scanned for viruses before it is accepted.
Signing in
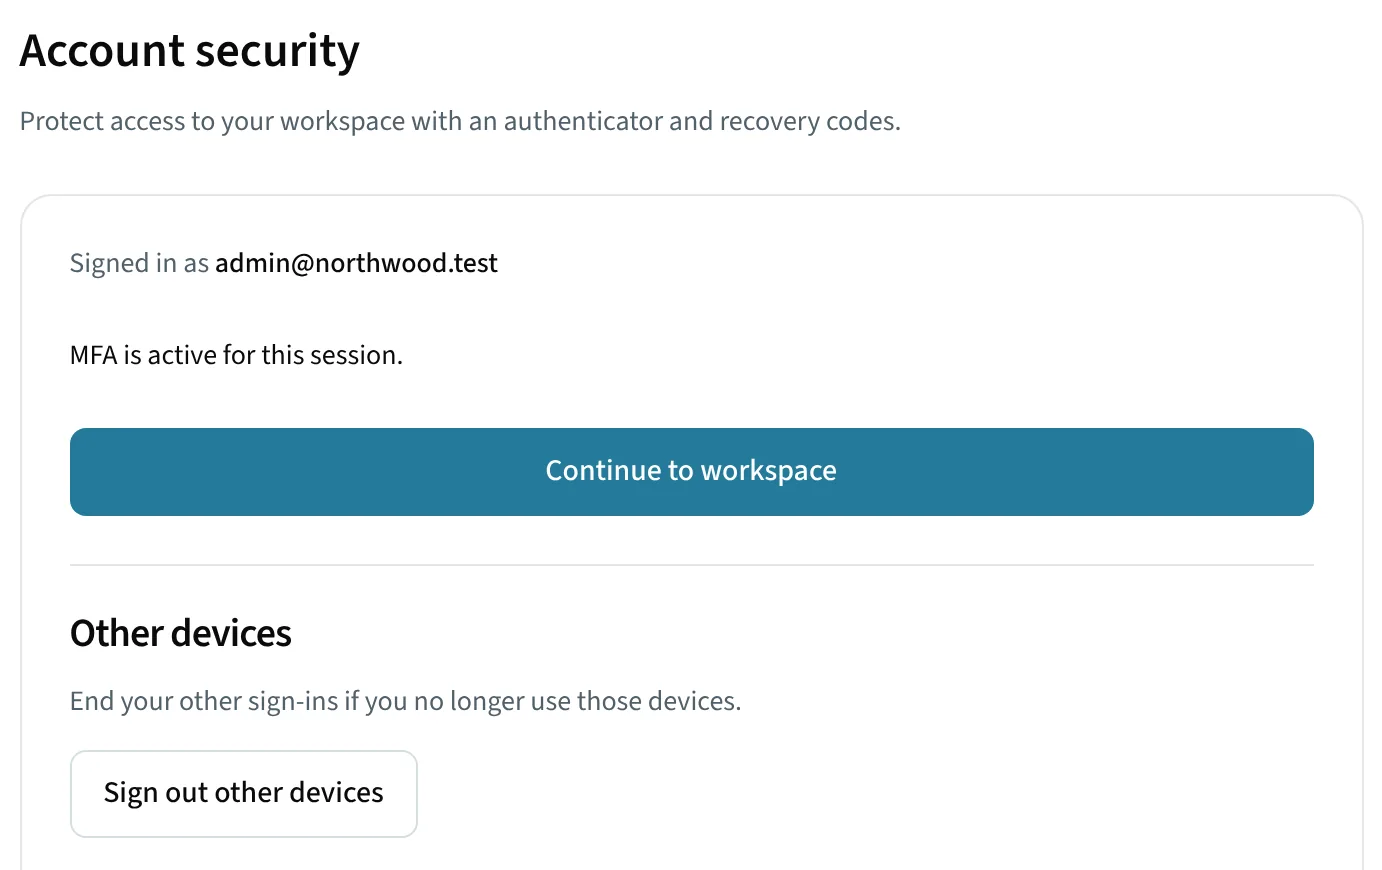
Two-factor authentication is required before anyone opens a clinical record. You sign in with your password and a code from an authenticator app, with one-time recovery codes in case you lose your phone.
Sessions end after a working day. Sensitive actions, such as signing a note, ask you to prove it’s you again. You can sign out your other devices from your account at any time.
Records that stand up
Nothing in Casely is ever deleted, and nothing is silently overwritten. Every change is kept with who made it and when.
A signed note can’t be edited. If something needs correcting, the correction is added as a permanent, attributed entry and the signed original stays exactly as it was. Client funds are kept in a ledger where an entry can only be reversed, never altered.
The assistant works for you
Casely drafts. You decide. Nothing the assistant prepares reaches a client’s record until a named person has reviewed and approved it, and every draft is kept apart from the clinical record until then.
The assistant only sees what the person using it is allowed to see.
Backups
Your data is backed up regularly, the backups are encrypted, and we test them by restoring from them.
UK GDPR
Casely is built to meet UK GDPR. You are the controller of your clients’ data and we process it on your instructions, under a written data processing agreement.
Your way out
You can take a complete export of your records at any time, in a form you can read without Casely. We’d rather keep you by being useful than by making it hard to leave.
Independent assurance
Casely is a new company, and we won’t show a badge we haven’t been awarded. Independent penetration testing is planned before general release. As we complete external assessments, we’ll publish them here.
If your practice or an instructing solicitor has a security questionnaire, send it to us. We’re happy to answer it in full.